Cybersecurity Awareness Month is a good reminder to check the basics, and one of the most overlooked is your domain. Many attacks on a business don’t start with a stolen password. They start with the domain: a lookalike name that fools your customers, a forgotten Domain Name System (DNS) record that points somewhere it shouldn’t, an email that appears to come from you, or a certificate that quietly expires.
Here are four checks to run this month. You can start all of them without new tools, and together they take about 15 minutes.
Do you know every domain you own, and who can change it?
Start with your registrar account. Confirm the contact details are current, more than one trusted person has access, and registrar lock is on, which blocks unauthorized transfers. Turn on two-factor authentication for everyone who can log in, so a stolen password isn’t enough to change your domains.
Then look at your DNS records. Old records are the quiet risk. A Canonical Name (CNAME) record that still points to a service you stopped using can let someone else claim that service and publish content under your subdomain. If your DNS runs through Cloudflare, the same review applies there.
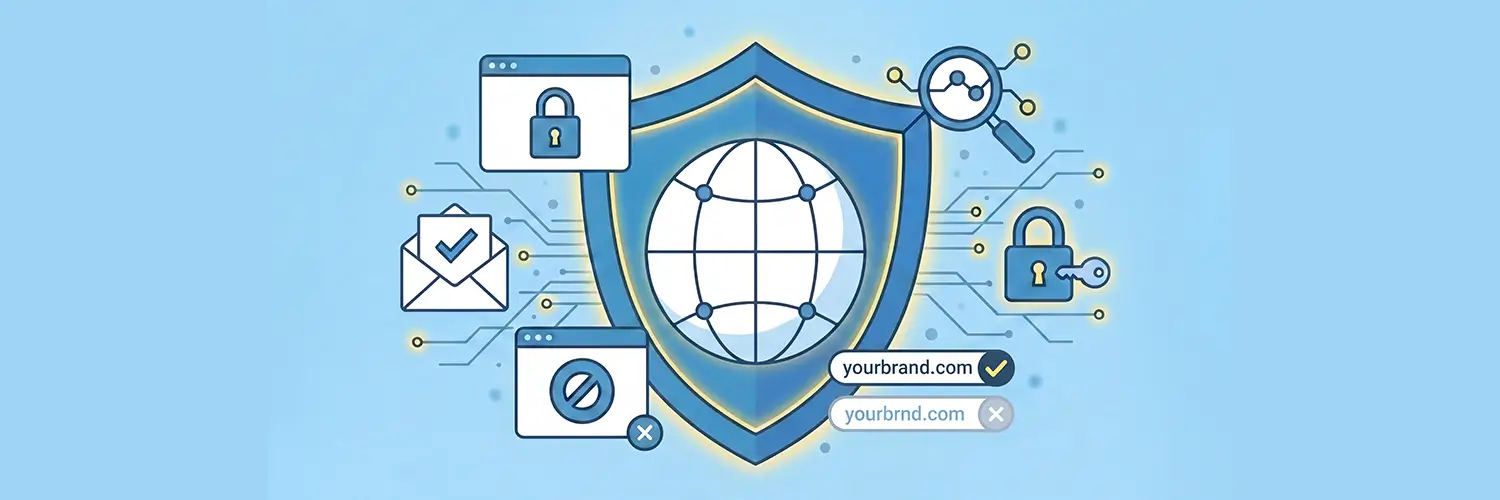
Finally, search for lookalikes: your name with a different extension (yourbrand.co instead of .com) or a one-letter change (yourbrnd.com). Attackers use these near-identical domains to send phishing emails, collect customer logins, and redirect payments. The email protections on your own domain don’t apply to them, because the lookalike isn’t your domain. If someone has registered one, your customers may find it before you do, so register the highest-risk variations defensively and monitor for new ones.
Can anyone send email as your domain?
Email is the easiest way to impersonate a business, because the “From” address is simple to fake. Three records work together to stop it. Sender Policy Framework (SPF) lists the servers allowed to send for you. DomainKeys Identified Mail (DKIM) signs your messages. Domain-based Message Authentication, Reporting and Conformance (DMARC) tells receiving servers what to do when a message fails those checks.
A DMARC policy of p=none only monitors. It sends you reports but blocks nothing. Real protection starts at p=quarantine and p=reject. Gmail and Yahoo already expect bulk senders to publish DMARC, so a record has been the baseline for a while. Don’t forget domains you don’t use, since parked and defensive domains need DMARC too.
Look up your domain’s DMARC record today. If it says p=none, check the reports to see which services send mail as you, then move to a stricter policy in steps. Our posts on DMARC policies, DMARC reports, and DMARC alignment walk through the details. If you’d rather not manage the rollout yourself, Managed DMARC Services handles policy setup, monitoring, and reporting.
What happens when a certificate expires on a subdomain nobody owns?
An expired Secure Sockets Layer (SSL) certificate, technically a Transport Layer Security (TLS) certificate, shows visitors a browser warning and can break integrations that depend on it.
The risk is growing because certificate lifespans are shrinking. Since March 15, 2026, public certificates can last no more than 200 days, and the limit keeps dropping. Even a multi-year subscription means reissuing and reinstalling certificates on that shorter cycle. Our post on the new shorter lifespans for SSL/TLS certificates explains the full schedule.
List every certificate you have, including those on staging sites and forgotten subdomains. Note each expiry date and who is responsible for renewal, and automate renewal where you can. If tracking them by hand isn’t realistic, SSL / TLS Certificate Monitoring is one way to keep watch.
What would an attacker find if they looked you up today?
Attackers map a business before they strike. They look for subdomains, domains left over from acquisitions or old campaigns, and tools that teams signed up for without telling IT, known as shadow IT.
You can run a version of that search yourself. Every publicly trusted certificate is logged in certificate transparency logs, which anyone can search. Look up your domain and see how many subdomains you don’t recognize. Attack Surface Monitoring does the same kind of mapping on an ongoing basis.
Google’s Chrome team recommended monitoring certificate transparency logs after attackers recently hijacked three country-code registries (.gh, .sl, and .as) and obtained unauthorized certificates. Google urged domain owners to watch for unexpected certificates on every domain they own, including parked and regional ones.
Your 15-minute checklist
- Lock down your domains: confirm registrar lock is on, two-factor authentication is enabled, and admin contacts are current. Remove old DNS records and search for lookalike domains.
- Look up your DMARC record and note the policy.
- List certificates that expire in the next 90 days.
- Search certificate transparency logs for subdomains you don’t recognize.
None of these checks are complicated, but each one closes a gap that attackers look for first. Run them once this month, put a reminder on your calendar to repeat them, and fix what you find in order of how easily it could be abused.
Ready to audit your domain security?
Talk with a 101domain expert about your domains, email authentication, and certificates.